SECURITY MODERNISATION & SECURE AI

Modernising security so AI can scale safely and confidently

Security Modernisation & Secure AI helps enterprises strengthen security foundations while enabling AI systems to operate safely, responsibly, and at scale.

When this
solution applies

This solution applies when:

What typically
breaks today

In many organisations, security and AI evolve on separate tracks. AI systems are piloted quickly, while security controls are applied later through reviews, exceptions, and manual approvals. As AI systems gain autonomy, access more data, and influence decisions, existing security models struggle to keep pace. The result is friction, stalled deployments, or over-restricted systems that never realise their potential. Security becomes reactive, and trust erodes across teams.

What we take
responsibility for

[01] Modernising identity and access for AI systems

We take responsibility for ensuring that identity and access models evolve to support AI and automation. This includes defining clear identities for AI systems and agents, enforcing least-privilege access, and ensuring permissions remain visible and controllable. Strong identity foundations prevent unintended access and enable accountability as AI systems scale.
[02] Embedding security into AI and data workflows

We take responsibility for integrating security controls directly into how AI systems access data and execute actions. This includes policy-driven enforcement, permission-aware access, and safeguards against unintended exposure. By embedding security into workflows, we reduce reliance on manual reviews and enable AI systems to operate safely in production.

[03] Designing secure agent behaviour and boundaries

We take responsibility for ensuring that agentic AI operates within clearly defined security boundaries. This includes scoping what agents can do, enforcing approval checkpoints for high-impact actions, and defining escalation paths. Secure agent design allows autonomy to increase without expanding risk.

[04] Enabling auditability and assurance by design

We take responsibility for making AI systems auditable as they operate. This includes generating evidence for access, decisions, and actions as a by-product of normal operation. Auditability is built into the system, enabling security, risk, and compliance teams to assess behaviour continuously rather than retrospectively.

[05] Balancing protection with delivery velocity

Where required, we take responsibility for ensuring that security modernisation improves speed rather than slowing it down. This means replacing ad-hoc controls with consistent patterns that reduce friction, shorten approval cycles, and allow teams to innovate with confidence.

What changes when this is done well

Controls evolve alongside AI initiatives, reducing late-stage rework.

Identity, permissions, and policies remain visible and enforceable.

Security is embedded into workflows rather than applied after the fact.

Assurance becomes continuous, not episodic.

Innovation progresses without increasing exposure.

CLIENT STORIES

What we have
seen in practice

Introducing identity‑first controls across AI systems and agents Making AI decisions auditable in regulated enterprise environments Embedding responsible AI controls without slowing enterprise delivery
REFERENCE ARCHITECTURES

Design that
support production

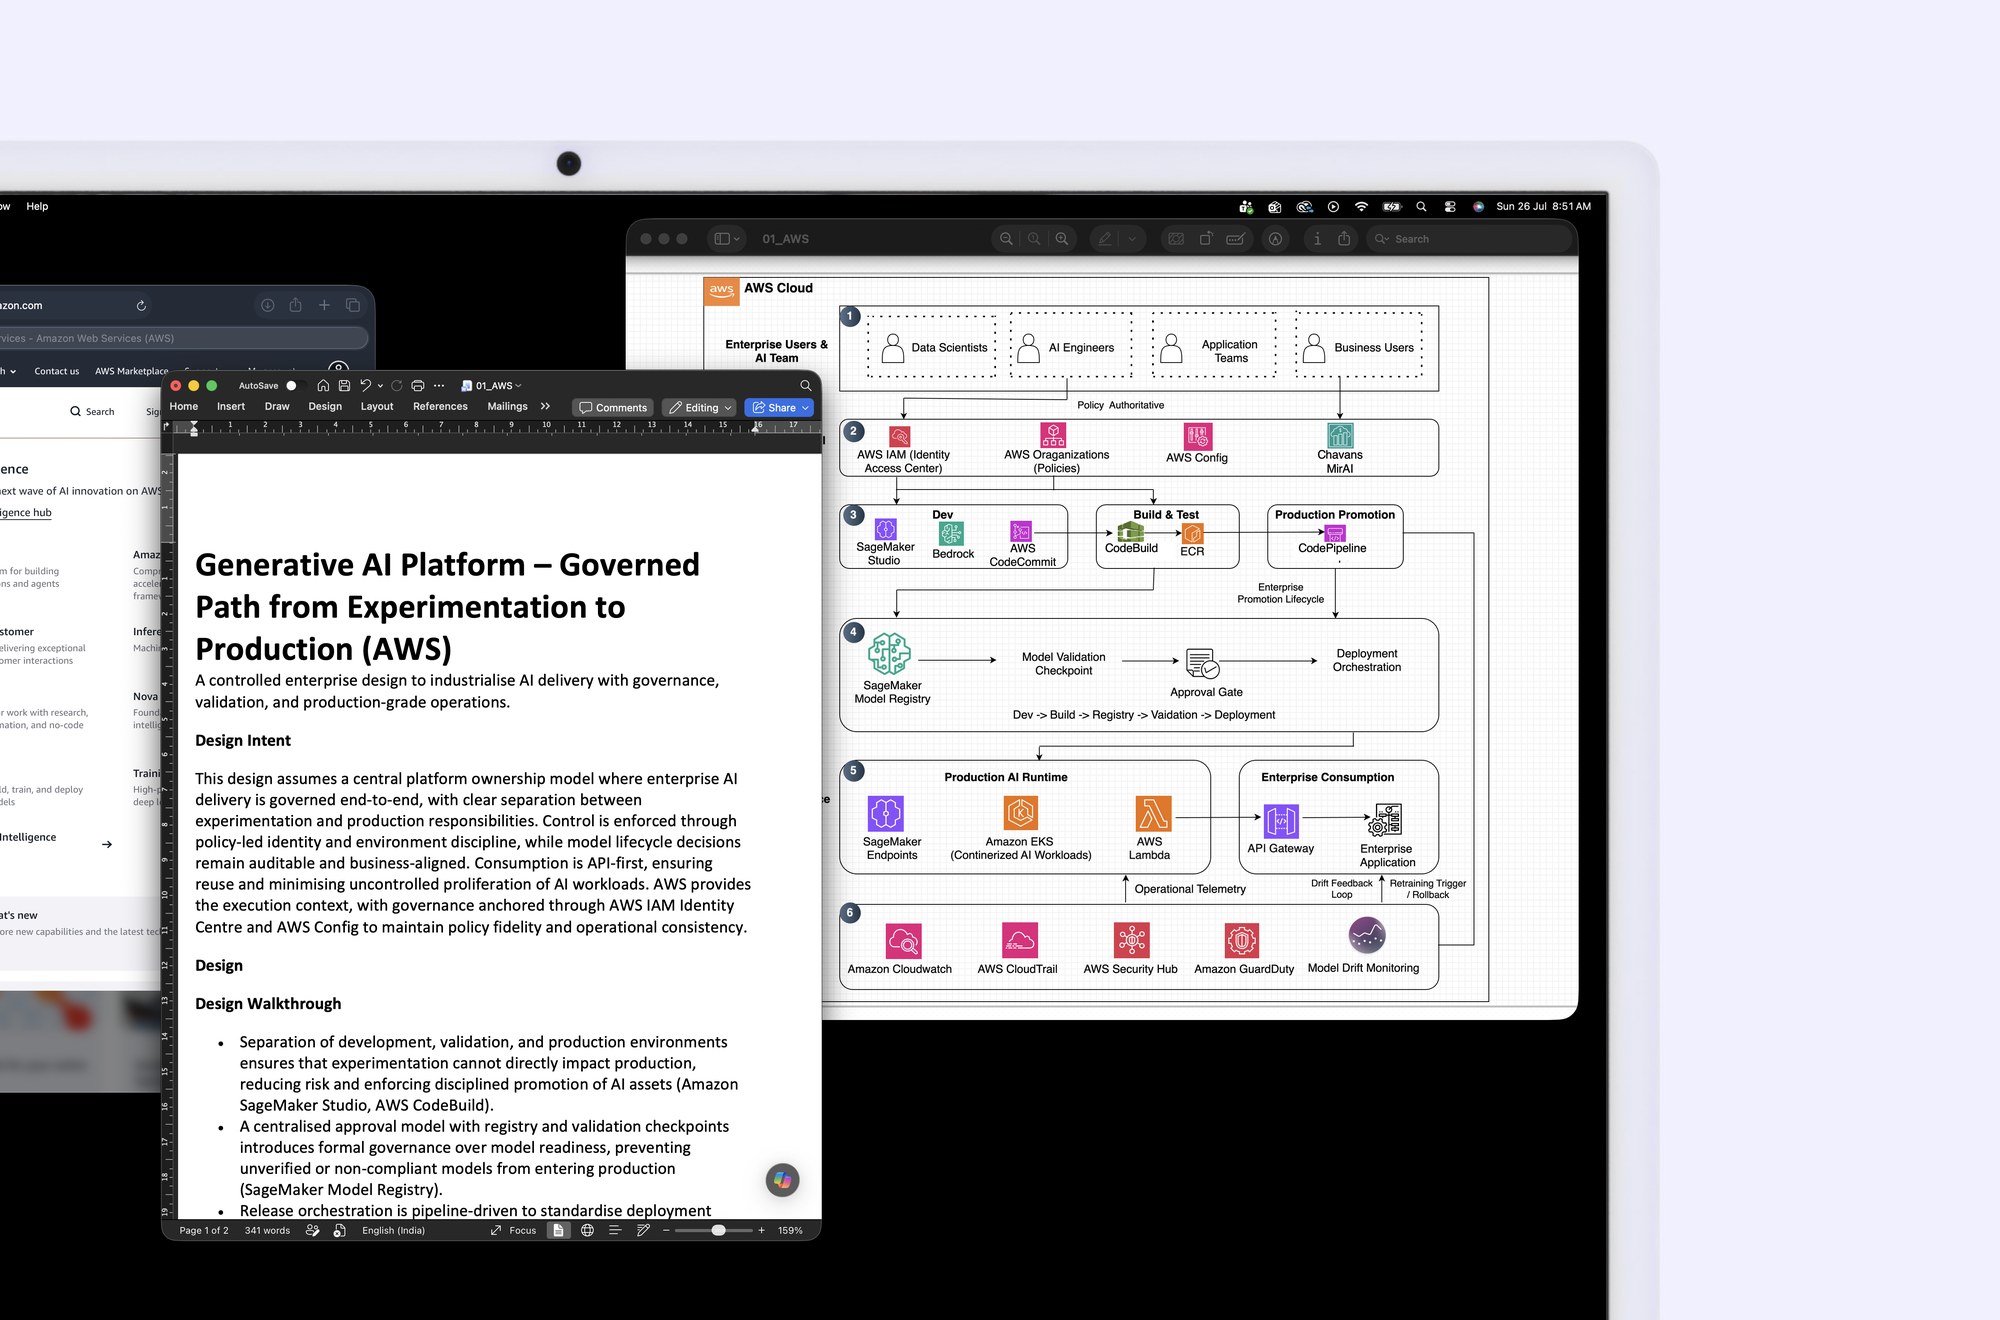
Generative AI Platform – Governed Path from Experimentation to Production (AWS): reference architecture document and diagram

Security-modernised AI environments rely on proven architectural patterns, including identity-first access models, policy-enforced data access, secure agent orchestration, and continuous monitoring for behaviour and compliance. These patterns ensure AI systems remain protected, observable, and auditable as they move into production and scale. View Reference Architectures

We design production-ready AI systems to operate within existing cloud, data, and security platforms, supported by our technology partnerships. View Partnerships

How engagements
start?

Engagements begin with structured working sessions focused on understanding current security posture, AI initiatives, and risk tolerance. These sessions identify where controls must evolve, how security should be embedded into AI workflows, and what changes will enable safe progress. The objective is alignment before enforcement.

How this connects
to other solutions

Security Modernisation & Secure AI connects closely with AI Adoption to Production, Agentic Workflow Automation, Enterprise Data & AI, and AI Operating Model. Together, these solutions ensure that AI systems are not only innovative, but secure, governed, and trusted throughout their lifecycle.

PERSPECTIVES

Related insights

[01] Secure AI Fails When Identity and Access Are an Afterthought [02] Why Security Must Evolve Before AI Can Scale

Start with clarity and context

A practical way to understand whether our approach fits your operating reality.

REQUEST AN INITIAL WORKING SESSION TALK TO A SPECIALIST